

What the FBI’s ARTEX warning means for production access
In several intrusions, attackers using ARTEX gained privileged access to cloud systems less than three hours after picking a target. Everton Bailey Jr. reported in The Dallas Morning News that the FBI’s Dallas office warned businesses about the tool on November 17. Designed for security testing, ARTEX uses AI agents to run multiple tasks in parallel. The FBI says criminals and state-linked groups have used it in attacks worldwide since at least August 2026. The Dallas Morning News report · November 13 FBI advisory
Think about the last time a vendor helped your team fix a production issue. Could that engineer still open your database today? If so, anyone who takes over the account inherits access that outlasted the job. Adaptive can help you decide in advance when that access expires, which customer details the engineer can see, and what evidence an investigator will have afterward.
What two ARTEX investigations tell us about access
During the ConnectWise Cloud Backup incident, Microsoft observed attempts to sign in to more than 2,250 customer tenants. The attackers used permissions customers had already granted to a vendor application. Because the application could sign in on its own, a security team looking only at employee logins could miss that activity. A cloud administrator reviewing this exposure should check which applications still have consent in the tenant and review their sign-in records. Microsoft’s investigation
In a separate campaign against South Korean financial firms, attackers stole personal information about roughly 67,000 people. Zscaler identified customer inquiry portals and services behind employee mobile apps among the targets. For a portal owner, the FBI recommends checking that each user is entitled to the specific customer record they request, limiting the fields returned, and watching for unusually high numbers of lookups in one session. Zscaler ThreatLabz research · FBI recommendations for portal owners, page 10
How Adaptive can limit a vendor’s production access
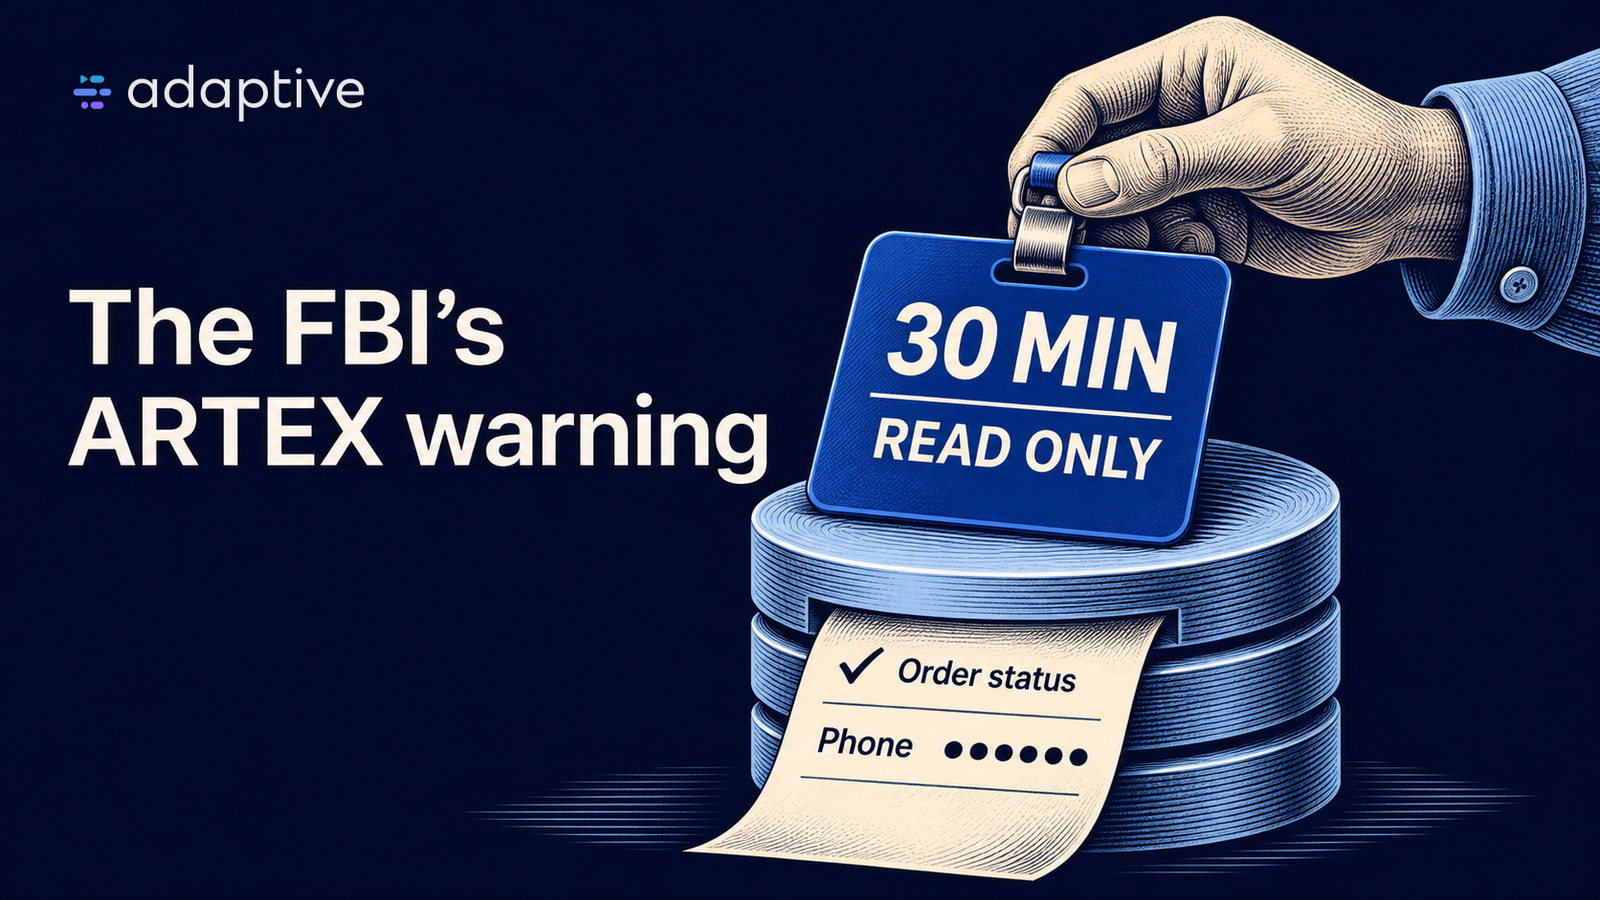
Suppose a supplier’s engineer is investigating a stuck order. The order status and the carrier’s last error are enough to diagnose it. The same PostgreSQL table also holds customer phone numbers. Here’s how the database owner could set up that support session through Adaptive.
- Give the engineer 30 minutes on the orders table. The engineer signs in through your identity provider with multifactor authentication. The owner approves a read-only role for that table. Adaptive brokers the connection without handing over a shared database password and revokes the temporary credential when time runs out. Tomorrow’s follow-up needs a fresh approval. Just-in-time infrastructure access
- Mask phone numbers in query results. A read-only role can still copy what it can see. With a column mask for the support role, the engineer can read the order status and carrier error while the customer’s full phone number stays out of the result. Adaptive data masking
- Tie each query to the person who ran it. Configure an alert for reads of a sensitive table and have Adaptive send it to the on-call channel. A responder can follow the link to the session and see the engineer’s identity, the database, and the query that triggered the alert. Audit events and alerting
When software does the work
The supplier’s nightly order-sync job can use its own workload identity, scoped to the database role it needs. Adaptive holds and rotates the database credential. Workload identity
If your support team uses an AI assistant to look up order status, limit it to the lookup tool, keep the database credential out of its context, and record each call under the assistant’s identity.
Start with one closed support ticket. Ask the database owner to show when the vendor’s access expired and find the last query under the engineer’s name. If an older shared login still reaches the database directly, retire it once the approved connection is working. Walk through your vendor access setup with Adaptive
- The Dallas Morning News report — https://www.dallasnews.com/business/technology/article/fbi-dallas-hackers-warning-22535909.php
- November 13 FBI advisory — https://www.ic3.gov/CSA/2026/261113.pdf#page=1
- Microsoft’s investigation — https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/
- Zscaler ThreatLabz research — https://threatlabz.zscaler.com/blogs/security-research/threat-actor-abuses-agentic-ai-pentesting-framework-target-south-korean
- FBI recommendations for portal owners, page 10 — https://www.ic3.gov/CSA/2026/261113.pdf#page=10


 |
 SOC2 Type II

